Title
What Happens When a Support Ticket Reaches ChatGPT? A Guide to Arceris AI Security Gateway
Description / SEO summary
Follow a support ticket from ChatGPT to a coding assistant and see how Arceris protects sensitive data, controls AI agent access, and routes work to approved models.
Categories
ai · developer-tools · legal-compliance
Content
A customer writes to support because a refund went to the wrong bank account. The ticket includes a payment reference, an IBAN, a screenshot, and several replies in Turkish. A support specialist opens ChatGPT and asks it to turn the thread into a short English handover for engineering. It is a reasonable use of AI. The engineer needs to know what went wrong. The model has little use for the customer’s bank details.
Now imagine that the support team has permission to use ChatGPT, engineering uses a coding assistant, and the company runs an internal language model for confidential work. Which tool should handle this ticket? What information should it receive? If someone later asks whether the IBAN reached an external provider, where would the security team look?
Arceris is a self-hosted AI security gateway built for decisions like these. To see how it works, follow the ticket through the browser, the engineering workspace, and the application that might eventually automate the handover.
What should leave the support specialist’s browser?
The first decision happens when the specialist clicks Send. Arceris can inspect supported AI sessions routed through the corporate network, including browser conversations with services such as ChatGPT, Claude, and Gemini. The company can define which information to mask, which requests to block, and which events to record for review.
For the refund ticket, a useful policy might allow the specialist to send the sequence of events while masking the IBAN. The resulting handover could still say that the customer updated their bank details on Monday and that Friday’s refund went to the previous account. Those dates matter to the engineer investigating the bug. The account number itself adds little to the diagnosis. A well-chosen redaction rule preserves that distinction and leaves the specialist with a usable summary.
The screenshot deserves a separate decision. A specialist might carefully remove the IBAN from the message and still attach an image of the original payment screen. Arceris can use optical character recognition to inspect text inside screenshots and PDFs. A security team could allow the typed summary and block an attachment containing bank details. From the employee’s perspective, the rule is easy to act on. They can finish the handover by sending the information engineering actually needs.
What changes when engineering opens a coding assistant?
The engineer receives the handover and asks a coding assistant to trace how the refund service selects a beneficiary. The sensitive material has changed. A stack trace might contain a service credential. A configuration file might hold a database password. Even when the engineer writes a careful prompt, the assistant may draw additional context from the workspace.
Arceris supports enrolled developer tools in terminals and editors, including Claude Code, Gemini CLI, and Cursor. Security teams can apply inspection and redaction to covered traffic from those tools. They can also restrict the file paths available to a coding agent. In the refund example, the engineer could let the agent work in the service’s source and test directories while keeping a directory containing production credentials outside its permitted scope.
Connected tools deserve the same attention. An engineering team might give its assistant access to an issue tracker through the Model Context Protocol (MCP). That connection has a clear purpose in this investigation. Arceris lets administrators approve or block MCP servers, so the team can decide which connections belong in the workflow. File access rules, MCP permissions, and outbound traffic inspection each answer a different question about what the assistant can read, reach, and send.
When should the work move to a local model?
Suppose the engineer discovers that the bug affects a payment partner whose involvement is still confidential. Removing names and account numbers may leave enough context to identify the partner. At that point, the security decision concerns the subject of the conversation as much as the individual values inside it.
Arceris supports topic-based policies and routing to approved local models. A company could allow routine translation on an external service and direct confidential incident analysis to a model running on its own infrastructure. Administrators can try a topic rule against sample prompts before enabling it for a group. That gives the people who own the workflow a chance to test ordinary language, internal terminology, and borderline cases.
A local deployment still leaves decisions for the company to make. Who may use the incident-analysis model? Which teams may upload case files? What happens if a response reproduces sensitive information from the material it received? Arceris can scope model access by user or group and mask sensitive values in supported streaming responses. The same review can therefore cover both the information submitted to a model and what appears on an employee’s screen.
What happens when the handover becomes an API call?
After handling enough refund tickets, the support team may decide to add a “Draft engineering handover” button to its own application. The employee gets a simpler workflow. Behind the button, a developer now has to choose a model, manage a provider credential, and account for repeated calls.
The Arceris API gateway gives applications a common endpoint and keeps provider credentials encrypted within the organization’s infrastructure. Administrators can control model access and set usage or spending limits. For a pilot, the team could approve one model and assign a budget before enabling the button. If a failed background job keeps retrying the same ticket, the budget gives the team a way to contain the cost while engineering investigates.
The security team can also reuse work it has already done. If the organization maintains payment-data rules in a data loss prevention system such as Symantec DLP, Arceris can submit prompts and uploaded files to that system through ICAP. The authenticated user accompanies the submission, allowing existing user-specific policies to apply to AI traffic.
How to tell whether the policy worked
A practical evaluation starts with a fictional refund ticket. Give it a test IBAN, a screenshot containing the same value, and a short timeline that an engineer would need. Ask a support specialist to produce the handover using their usual browser. Then ask an engineer to investigate it with their usual coding assistant. Have both people judge whether they can finish their work with the controls enabled.
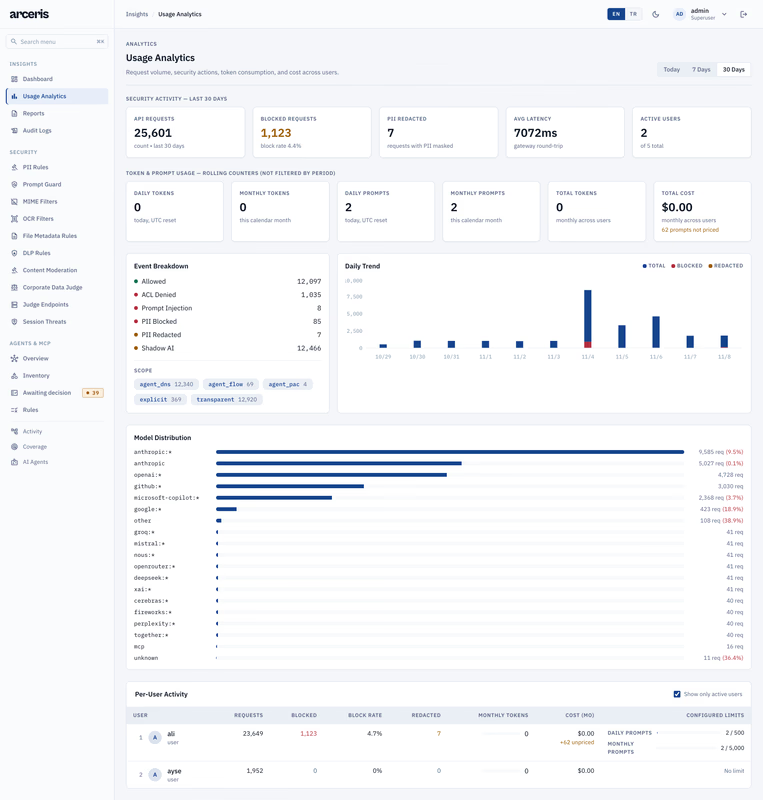
Check the results at each step. Did the summary preserve the order of events? Did the screenshot trigger the intended rule? Could the coding assistant still read the test fixture it needed? Could a reviewer identify the user, the policy, and the action taken? Arceris records policy interventions and can export events to a security information and event management system, giving the reviewer a place to start.
Finally, repeat the exercise with a ticket containing no sensitive data. That second run tells you something a successful block cannot: whether an ordinary support request still moves smoothly from the customer’s message to the engineer who can fix the problem. Teams planning their own evaluation can explore the inspection, routing, and developer controls in the Arceris AI Security Gateway product guide.